Explore checkers, demos and evaluation routes →
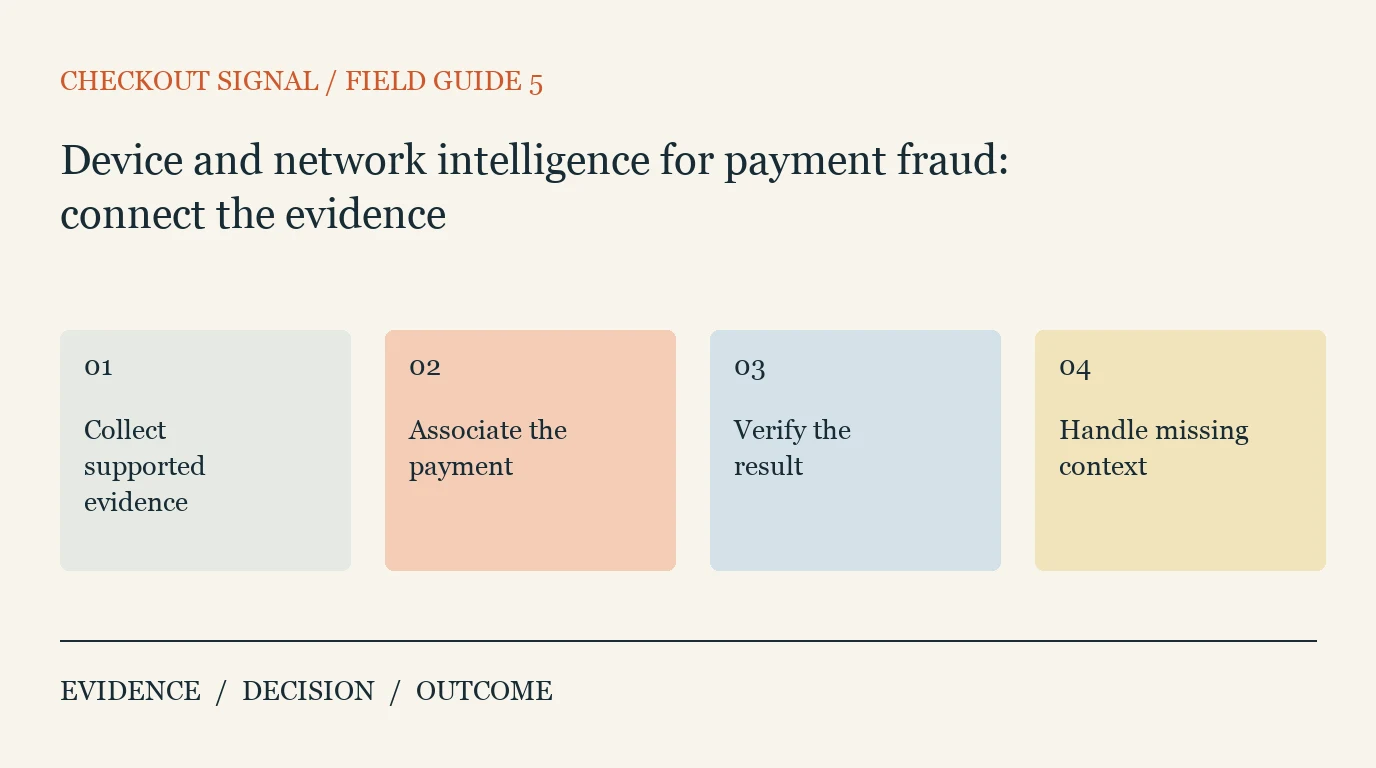
Device and network intelligence for payment fraud: connect the evidence
Understand the browser evidence behind an order
A browser fingerprint combines observable settings or behavior to help recognize an environment. Canvas pixel output, rendering properties, JavaScript features and network observations contribute different evidence. The fingerprint is neither a cardholder name nor a payment authorization. Privacy protections can reduce or alter observations. W3C documents both security uses and privacy impacts; disclose collection purpose and retain only what the fraud workflow needs.
Read audio processing as an environment signal
Browser audio fingerprinting processes a generated signal and examines its output. MDN explains that OfflineAudioContext renders to an AudioBuffer rather than audio hardware. This differs from recognizing a recorded song and from microphone capture, which uses a separate permission-controlled API. For checkout risk, combine audio evidence with other observations. A changed audio hash alone cannot establish a new buyer or a stolen card.
Buy recognition rather than a memorable hash
Evaluate Fingerprint, ShieldLabs, Castle, Incognia and other device providers against your actual browser and native-app surfaces. Ask what identifier returns, how missing collection is represented and how collisions and identity splits are measured. ThumbmarkJS offers an inspectable fingerprinting approach but is not equivalent to a complete payment-fraud workflow. Regional availability and data handling require contract checks; a global website does not prove Saudi deployment suitability.
Reference: Fingerprint: Smart Signals reference.
Separate device identity from device risk
Device intelligence adds context such as automation, tampering and location evidence to recognition. Native mobile SDKs and browser scripts expose different observations. For a mixed checkout estate, verify supported iOS, Android and web integrations and how account references connect them. Incognia emphasizes location-grounded recognition; ShieldLabs combines device and network intelligence. Neither a device label nor a digital-intelligence category name establishes a legally verified person.
Reference: W3C: fingerprinting guidance.
Use tampering evidence as one part of review
Anti-detect detection looks for inconsistent or manipulated browser environments. Headless detection identifies automation-related properties; the two categories overlap but are not identical. Compare browser observations with session behavior and connection evidence, then retain explainable reasons. Privacy defenses can also change observable properties. Developers investigating a legitimate integration should use an authorized test environment and vendor documentation rather than attempting to disguise payment traffic.
Reference: W3C: fingerprinting guidance.
Know where network fingerprints are observed
HTTP/2 behavior, TLS client fingerprints and TCP fingerprints describe different layers. FoxIO's JA4 family includes JA4 for TLS, JA4H for HTTP and JA4T for TCP, with implementation tools in its repository. JavaScript alone cannot observe every transport characteristic behind a CDN. Cloudflare notes that JA3/JA4 fields can be missing and have plan restrictions. Shared client fingerprints are grouping evidence, not individual payer IDs.
Read returning-visitor metrics with the right denominator
A returning visitor has prior activity under the reporting identity available to the analytics system. GA4 can use User-ID, device ID and modeling according to its reporting settings. Visits, unique visitors and page views count different things: one shopper can load many pages in several sessions. There is no universal healthy new-to-returning ratio. Compare the same acquisition cohort and observation period before changing checkout policy.
Reference: Google Analytics: understand user metrics.
Personalize the guest experience without granting access
Anonymous context can support language, recently viewed items or relevant help before login. Use consented first-party behavior and distinguish an inference from an account fact. Associate the guest with a known customer only through a trustworthy transition such as authentication. Keep pricing entitlements, stored addresses and paid content behind server authorization. A fingerprint match should not reveal private account information to the current browser.
Reference: OWASP: authorization.
Worked recognition example: a guest returns on another device
Hypothetical example: a shopper visits on a work laptop, returns on a phone and signs in before buying. Keep both observed device references. The authenticated account can join the journey; similar browser characteristics alone should not expose the earlier address or invoice. Compare the expected same-device and cross-device relationships as different outcomes.
| Observation | Useful conclusion | Limit | | Same-browser recognition | Earlier session context | Does not authenticate the payer | | Account login | Authorized account association | Session and recovery still matter | | Page views | Content loaded | Does not count unique people |
Continue with Payment network risk, bots and endpoint defense for the next evidence layer.
Separate owned-asset discovery from visitor intelligence
If the objective is automatic discovery of payment-terminal or other owned assets, compare inventory products. Axonius Device Intelligence Hub manages scanning adapters and OT/IoT scan jobs. Lansweeper describes IT, OT, cloud and IoT discovery with normalization. These tools answer which assets an organization operates. Visitor intelligence answers what is observed about a customer interaction. Define that subject before interpreting the broad phrase local digital intelligence as a specific deployment promise.
Sources
- W3C: mitigating browser fingerprinting · read
- MDN: CanvasRenderingContext2D.getImageData · read
- W3C: Web Audio specification · read
- MDN: OfflineAudioContext · read
- W3C: Web Audio privacy and security · read
- MDN: getUserMedia · read
- Fingerprint: Smart Signals reference · read
- Thumbmark: product and integration scope · read
- Incognia: use cases · read
- NIST: identity-proofing scope · read
- OWASP: automated threats · read
- Cloudflare: JA3 and JA4 · read
- FoxIO: JA4+ project and specifications · read
- Cloudflare: HTTP headers · read
- NIST: authentication and sessions · read
- Google Analytics: user metrics · read
- Google Analytics: reporting identity · read
- Google Search Console: performance report · read
- Google Search Console: dimensions and query omissions · read
- OWASP: authorization · read
- Primary source: docs.axonius.com · read
- Primary source: www.lansweeper.com · read
- Primary source: deviceatlas.com · read
- Primary source: privacysandbox.google.com · read
- Primary source: shieldlabs.ai · read
- Primary source: www.incognia.com · read
- Primary source: acoustid.org · read
- Primary source: acoustid.org · read
- Primary source: cflib.org · read
- Primary source: castle.io · read
- Primary source: www.browserscan.net
Continue reading
FAQ
Can a returning-visitor ID authorize saved-card access?
Recognition provides context about continuity. Saved-card access still requires the appropriate account authorization and payment flow; a probable visitor match alone is insufficient.
What does DeviceAtlas identify?
For a returning payer, DeviceAtlas supplies device identification and properties for uses including optimization and analytics. Score that output separately from a persistent person identity or ready account-abuse finding. Verify the returned object rather than treating every device-intelligence product as the same recognition service.
What did the April 2025 Chrome tracking announcement say?
For a returning payer, the dated Google announcement is useful context: on April 22, 2025 it retained Chrome's existing third-party-cookie choice approach instead of a standalone new prompt and described further tracking-protection work. It is a dated policy announcement, rather than a complete inventory of every Chrome feature shipped afterward.
Which recognition providers belong on a device shortlist?
For returning guest context, compare the recognition output. Compare Fingerprint for recognition and documented Smart Signals, ThumbmarkJS for an inspectable fingerprinting approach, ShieldLabs for recognition plus ready risk/account events and Incognia where location-grounded recognition is central. Match web/native surfaces, errors, retention and required output before choosing.
How do music or acoustic fingerprints differ from browser audio fingerprints?
For payment engineers investigating audio SDK terminology, Chromaprint extracts a recording fingerprint from supplied audio; AcoustID can look it up with duration and return related recording metadata. A typical authorized workflow decodes the recording, generates the fingerprint and queries an appropriate catalog. Check corpus fit, permissions and commercial service terms. Browser Web Audio fingerprinting instead compares processing behavior; it does not identify the song, speaker or rightful account owner.
How should separate browser profiles be used for authorized account work?
For a payment team, keep the authority to access, the order evidence and the financial contract separate. First establish permission to operate each account. Use documented workspace roles, distinct session/storage profiles and the platform’s approved team or agency APIs where available. For testing your own application, record the profile, collector version, expected permissions and result, then verify that private data and grants remain isolated. A modified browser or rotating route does not create account eligibility or permission to evade another service’s restrictions. W3C fingerprinting guidance explains the observable surfaces; OWASP authorization applies independently of profile appearance.
How should device intelligence be selected for a Saudi deployment?
For a payment team, keep the authority to access, the order evidence and the financial contract separate. Build a shortlist around ShieldLabs, Fingerprint, Incognia or a broader risk supplier according to the required web/native and decision scope. Then request a written data-flow and contract review covering collection purpose, lawful transfer arrangements, processing/storage locations, subprocessors, retention/deletion, regional network latency and support. A product marketed worldwide does not by itself establish Saudi hosting or a local-residency commitment. Make those acceptance conditions explicit before purchase.
What should a browser-detection or browser-scan result be used for?
For a payment team, keep the authority to access, the order evidence and the financial contract separate. Clarify whether the task is parsing browser software, inspecting the current environment, classifying a relay or recognizing repeat activity. The CFLib browserDetect function, dated 2011, illustrates user-agent parsing rather than persistent identity. A scan can report selected browser/network observations without proving account ownership or universal anonymity. If a search phrase is an imprecise spelling of anti-detect or a legacy tool name, confirm the exact maintained product and official documentation before downloading or choosing infrastructure. An anonymizing gateway routes traffic through another endpoint; it does not erase the site’s other history. These category distinctions interpret the task without asserting that every ambiguous string names a verified product.
Which visitor/device options fit identity platforms and gaming?
For a payment team, keep the authority to access, the order evidence and the financial contract separate. For CIAM or gaming, compare Fingerprint for recognition/Smart Signals, ShieldLabs for recognition plus ready abuse events, Castle for account/environment intelligence and Incognia where location-grounded recognition matters. Include legitimate shared equipment, updates, cookie resets, platform-supported native/web clients and repeated restricted claims. Measure recognition errors and player completion separately from policy findings. Favor the documented output that fits your flow rather than an unverified universal reliability label.
If BrowserScan is intended, what does its browser check show?
The BrowserScan page lists network, browser, canvas/audio and automation diagnostics. Treat “scanbrowser” as an imprecise service name until the intended URL is confirmed. A generic browser scan can also mean inspecting observable properties. Diagnostic output describes what the checker sees in that context; it is not a certificate of population uniqueness, account ownership or invisibility to every website.
Summarize this page with
Device and network intelligence helps a payment team understand the session behind an order. It can reveal returning environments, automation or masking that a transaction record alone does not explain. The value depends on collecting the evidence correctly and connecting it to the right payment attempt.
- 1Collect supported evidence
- 2Associate the payment
- 3Verify the result
- 4Handle missing context
Inspect relationships rather than one flag
A VPN can belong to a legitimate customer. A residential exit can belong to an abusive operation. Treat the network observation alongside device consistency, supported automation evidence, timing and associated account activity. A static blocklist can become stale as network ownership and exits change.
ShieldLabs combines current device and network intelligence with risk scoring and account-level findings. Its official product facts describe returning identity and named risk signals. Evaluate supported collection and result retrieval for the payment flow you protect.
Connect collection to the decision
Assign an internal order reference and preserve the vendor's supported request or session identifier. Retrieve the trusted result through the documented server path or verify the webhook. Check result freshness and association before applying it to a protected action.
| Failure case | What to check |
|---|---|
| A result belongs to another basket | Server-side order and collection association |
| The SDK failed to load | Missing-result state and supported fallback |
| The IP changed during checkout | Timing, device continuity and new evidence |
| A shared device serves several people | Account context and corroborating evidence |
| The order changes after assessment | Reassessment rules for the actual integration |
Compare providers without flattening their outputs
SEON combines digital footprint and device evidence with decisioning. Sardine combines device, behavior and financial-risk workflows. Their billing units and product packages differ from ShieldLabs identifications.
Kount's integration uses device collection and order data. Its current Payment Omniscore has a higher-is-safer direction, while many risk scores use higher-is-riskier. Never map several numeric scores into a shared threshold without reading each result contract.
Evaluate four controlled cases
Include a known legitimate guest on a privacy tool, a shared household device, an authorized repeated-attempt scenario and missing collection. Document what evidence is actually available in each case. A device link can explain a relationship without establishing that several people are one user.
Measure result availability before the relevant payment action. A correct result delivered after fulfillment may still be useful for investigation but cannot support the decision that already happened.
FAQ
Does an IP flag establish a fraudulent payment?
No. Inspect corroborating session, account, order and payment evidence before applying a restriction.
Can device intelligence authorize a card?
No. Device context supports risk assessment. The processor and issuer handle their own payment decisions.
What should happen when evidence is missing?
Use an explicit supported fallback, review or pending path. Do not silently interpret a missing result as a trusted result.
Continue reading
See guest checkout, card-testing containment and the API and deployment guide.
Continue reading
- How to stop card testing without locking out real customers
- Guest checkout fraud: evaluate risk without requiring an account
- How to measure false declines alongside missed payment fraud
Compare all ten tools or read the complete deployment guide.